
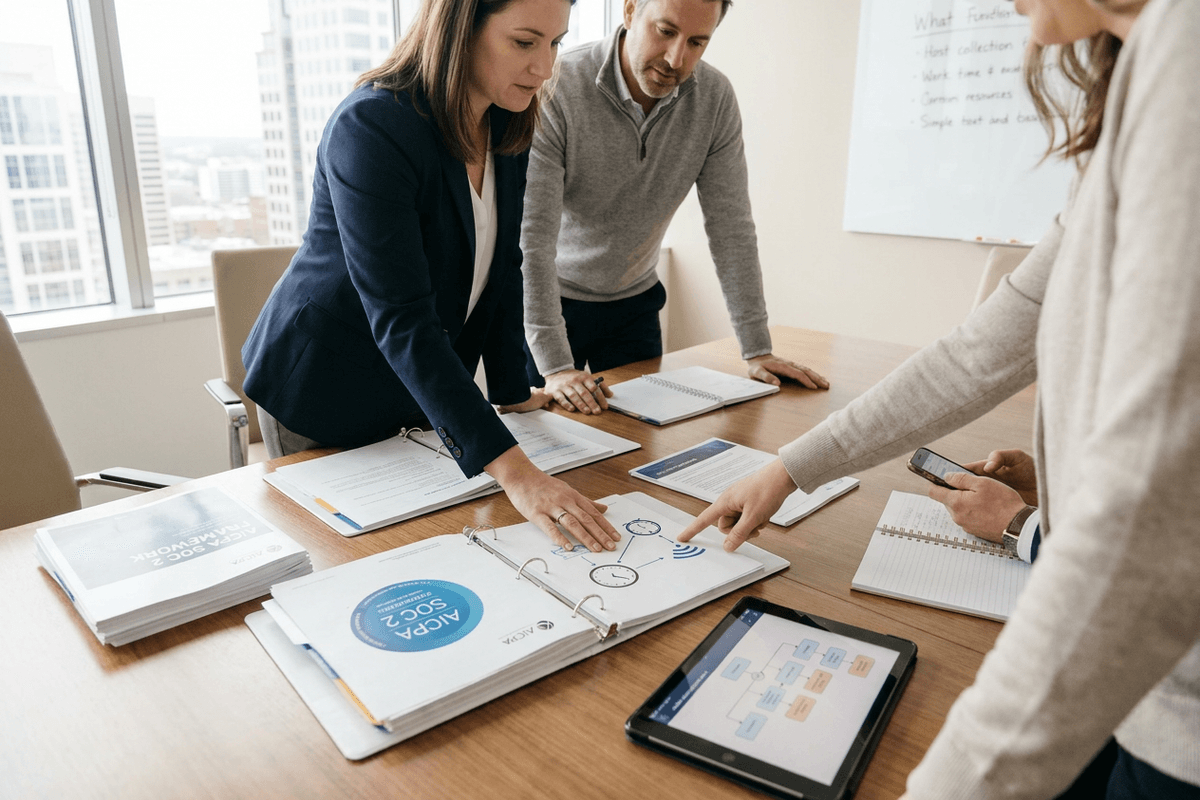
For nearly a decade, the AICPA’s Trust Services Criteria have functioned as the undisputed currency of enterprise credibility in North America. A clean SOC 2 Type 2 report was the universal hall pass that allowed SaaS startups to sell to Fortune 500 enterprises, permitted cloud providers to host critical infrastructure, and gave risk committees peace of mind across complex multi-tenant environments. Yet, while the baseline 2017 Trust Services Criteria were engineered for an era dominated by cloud migration and basic API ecosystems, enterprise software has fundamentally outpaced that architecture. Today, code repositories deploy autonomous agents, proprietary workflows depend on large language models (LLMs), and automated decision pipelines dictate everything from credit underwriting to medical claims routing.
Acknowledging this tectonic shift, the AICPA has formally released an exposure draft proposing targeted revisions to the SOC 2 Trust Services Criteria, as reported by the Journal of Accountancy. Designed to enhance clarity, usability, and technical precision for attestation practitioners, the proposed updates mark the most consequential recalibration of SOC 2 standards in years—formally dragging algorithmic governance, model risk management, and automated control oversight into the core assurance lexicon.
The Modernization Imperative: Moving Beyond Static ITGCs
The core tension in IT attestation over recent years has been the friction between deterministic systems and probabilistic models. When the 2017 Trust Services Criteria were established, evaluating system "processing integrity" (the PI series) or "security" (the CC series) centered primarily on deterministic inputs and outputs: Did the code execute as authorized? Did unauthorized users penetrate the perimeter? Was sensitive customer data isolated in multi-tenant databases?
In modern service organizations, however, software is no longer entirely deterministic. Autonomous microservices make probabilistic inferences, third-party foundation models ingest customer datasets via retrieval-augmented generation (RAG) pipelines, and algorithmic logic recalibrates dynamically based on continuous learning loops. Auditing these environments using static sampling techniques—such as reviewing twenty ticket approvals or checking quarterly access reviews—has increasingly left gaping blind spots in enterprise risk management.
"The exposure draft directly confronts the reality that artificial intelligence and automated decision systems are no longer aspirational add-ons—they are embedded in the critical infrastructure of service organizations, demanding rigorous internal controls that auditors can consistently evaluate."
By modernizing the criteria, the AICPA aims to eliminate the ad-hoc, fragmented custom criteria that leading risk advisory practices have been forced to invent to cover clients' AI capabilities. The proposed changes provide a standardized framework for CPAs evaluating internal controls over information systems across the five classic Trust Services categories: Security, Availability, Processing Integrity, Confidentiality, and Privacy.
Core Focus Areas: AI Governance, Automated Logic, and Model Monitoring
The proposed revisions expand guidance across several foundational areas, introducing heightened scrutiny of how algorithms are conceptualized, trained, deployed, and monitored over time. Rather than generating an isolated, disconnected "AI criteria" silo, the AICPA has integrated these emerging risk factors directly into the Common Criteria (CC series) and Processing Integrity category.
1. Model Lineage and Training Data Governance
Under the revised proposals, service organizations utilizing machine learning or generative AI must demonstrate verifiable controls over the provenance, integrity, and confidentiality of their training data. This includes robust mechanisms to prevent unauthorized data ingestion, mitigate data poisoning risks, and protect customer intellectual property from being inadvertently incorporated into global model training corpuses without explicit consent.
2. Safeguards Against Model Drift and Output Decay
Unlike conventional software, which only changes when a developer commits a new build, AI models degrade over time as real-world data patterns diverge from baseline training datasets. The updated criteria emphasize continuous model monitoring—requiring organizations to demonstrate automated alerts and active management interventions when performance thresholds, latency, hallucination rates, or algorithmic biases drift beyond acceptable tolerances.
3. Automated Decision-Making and Human-in-the-Loop Oversight
When an algorithm possesses autonomous or semi-autonomous execution authority—such as automatically modifying user permissions, routing financial disbursements, or filtering high-stakes transactions—the proposed criteria demand documented boundaries. Auditors must evaluate whether organizations maintain explicit "circuit breakers" and verify that human-in-the-loop review protocols operate effectively for edge-case anomalies.
Comparative Analysis: The Evolution of SOC 2 Trust Services Criteria
To understand the depth of this shift, practitioners should review how the proposed exposure draft recalibrates core audit dimensions relative to the historical 2017 framework:
| Audit Dimension | 2017 Trust Services Criteria | Proposed Modernized Criteria |
|---|---|---|
| Core Focus | Deterministic cloud architecture, static logical access, and network infrastructure. | Probabilistic systems, algorithmic integrity, API ecosystems, and autonomous workflows. |
| Processing Integrity (PI) | Evaluates complete, valid, accurate, timely, and authorized data processing. | Expands to cover input validation for neural networks, synthetic data generation, and model calibration. |
| Change Management | Standard code review, pull request approvals, staging environments, and deployment sign-offs. | Incorporates model fine-tuning, hyperparameter adjustments, prompt template updates, and weight changes. |
| Third-Party Vendor Risk | Subservice organization evaluations (e.g., AWS, Azure, co-location data centers). | Includes external model-as-a-service providers (MaaS), API dependencies, and foundation model licensing risk. |
| Evidence Expectations | Static screenshots, configuration exports, change tickets, and point-in-time samples. | Continuous monitoring telemetry, model drift dashboards, synthetic testing suites, and data lineage logs. |
Operational Repercussions for CPA Attestation Practices
The practical implications for public accounting firms specializing in SOC and IT risk advisory are immediate. As these revisions progress through the public comment period toward final codification, practitioners must rethink their audit methodologies, staffing configurations, and field execution strategies.
1. The Demise of the Generalist IT Auditor
For decades, generalist staff auditors with a baseline understanding of Active Directory, AWS IAM policies, and JIRA workflows could execute standard SOC 2 control testing. That operating model is now obsolete. Evaluating whether an organization’s AI monitoring controls satisfy Processing Integrity requires understanding statistical significance, data pipeline architectures, and algorithmic validation tools. Accounting firms will increasingly need to recruit dual-competency professionals who bridge computer science, data engineering, and attestation standards.
2. Re-scoping Engagements and Managing Client Expectations
Many SaaS companies have aggressively incorporated AI features into their core product marketing over the past two years without fully considering the audit implications. Under the revised criteria, service organizations will no longer be able to carve these systems out of their System Description without raising severe red flags for enterprise procurement officers. Attestation teams must proactively consult with clients to expand their Type 1 and Type 2 scopes, directly impacting billing realizations, testing timelines, and engagement planning.
3. Redefining Subservice Organization Due Diligence
Virtually no mid-market software company builds its own foundational models from scratch; they layer fine-tuned models and proprietary vector databases on top of third-party infrastructure such as OpenAI, Anthropic, or specialized AWS Bedrock configurations. Under the proposed enhancements, auditors must evaluate whether service organizations maintain adequate controls to govern API reliability, rate-limiting failures, and data privacy commitments enforced by these external AI vendors.
Strategic Action Steps: Preparing for Codification
While the AICPA evaluates public commentary, progressive accounting firms and their enterprise clients should avoid a passive posture. Firms should immediately initiate a multi-phase readiness strategy:
- Submit Public Comments: Engage actively with the AICPA’s exposure draft. Practitioners in the field possess ground-level insight into what testing procedures are practically verifiable versus those that introduce unworkable ambiguity into AT-C Section 205 attestation engagements.
- Perform AI Inventory Audits: Require clients to assemble comprehensive algorithmic registries. Before controls can be audited, organizations must map where autonomous logic, predictive scoring, and machine learning components touch customer data within the defined system boundaries.
- Update Internal Working Paper Templates: Risk advisory practices should begin drafting modified risk and control matrices (RCMs) that map to the proposed criteria, ensuring testing programs are pre-populated with model monitoring, data governance, and prompt architecture controls.
- Accelerate Continuous Testing Tooling: As controls transition from manual administrative policies to algorithmic automation, manual audit sampling becomes cost-prohibitive. Firms must invest in programmatic audit tools capable of ingesting automated telemetry and continuous compliance logs.
Conclusion: Assurance in the Algorithmic Era
The AICPA’s initiative to modernize the SOC 2 Trust Services Criteria represents a vital evolution for the public accounting profession. In an enterprise economy increasingly dominated by non-transparent, autonomous software, the market’s hunger for independent, credible, and standardized assurance has never been greater. By expanding SOC 2 to encompass artificial intelligence governance, automated logic, and model monitoring, the accounting profession reaffirms its foundational role as the ultimate arbiter of enterprise trust.
Firms that embrace these proposed criteria as an opportunity to upskill their teams, elevate their technical rigor, and guide clients through the complexities of algorithmic governance will capture outsized market share in the attestation space. Those that treat the revisions as a mere administrative compliance checklist risk issuing reports that fail to address the defining operational risks of modern enterprise technology.